

HR Data Security: The Access Problem Hiding in Plain Sight
The Problem With HR Data Security That’s Hiding in Plain Sight
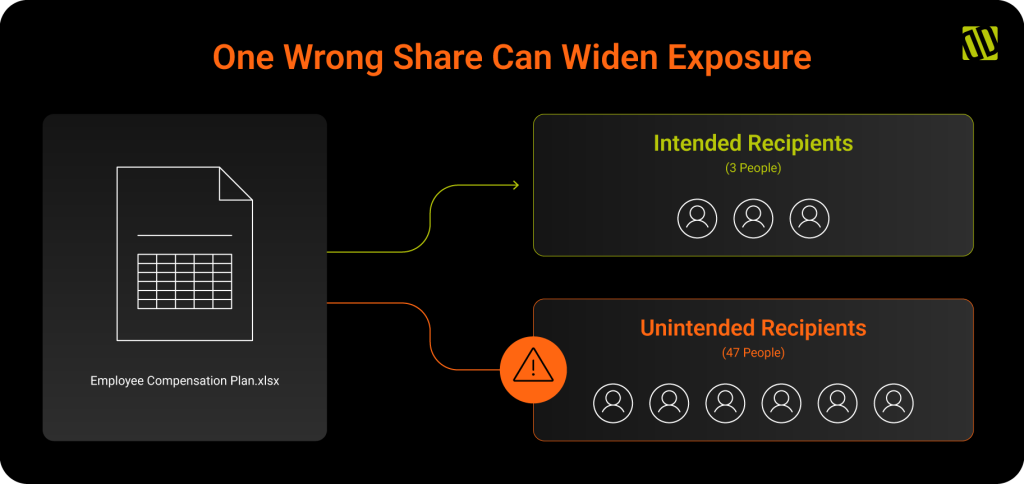
Imagine you work in HR and are preparing a spreadsheet containing confidential employee information for a specific group of managers. When it’s time to share the file, you accidentally select the wrong email group and send it to far more people than intended.
Scenarios like this show how easily sensitive HR information can be exposed. The problem is not always weak access controls. Often, the bigger challenge is maintaining a clear understanding of where confidential information lives, who can access it, and whether that access is still appropriate.
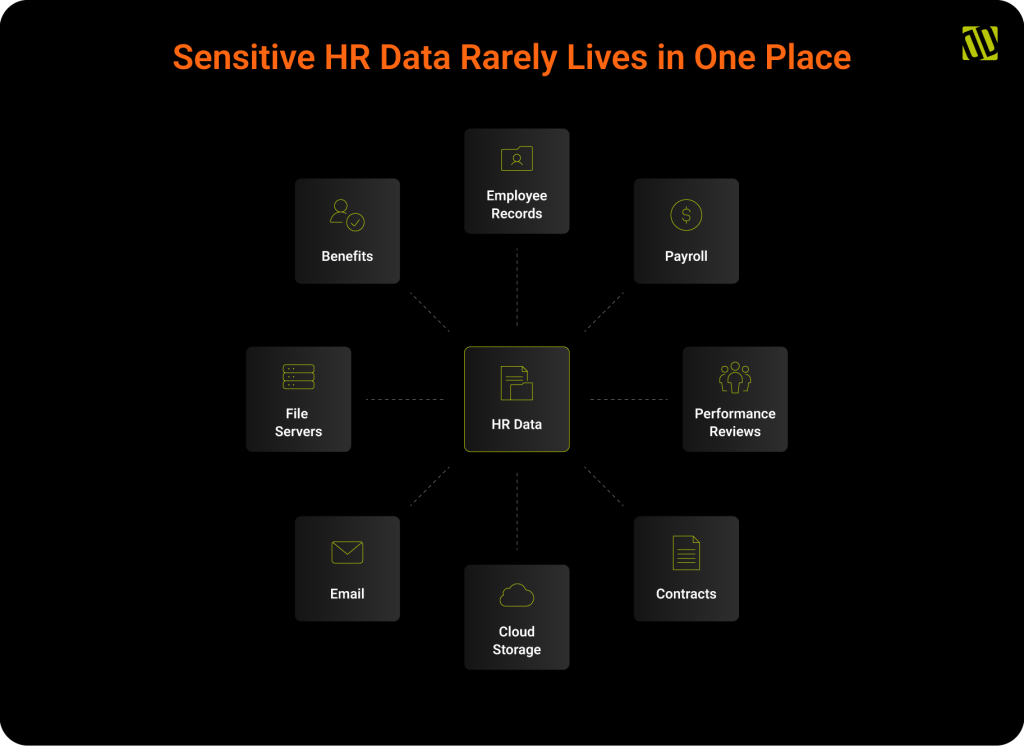
HR teams hold some of an organization’s most sensitive information, including employee records, payroll data, performance reviews, and other confidential documents. That information may be distributed across different systems and storage locations, while access permissions accumulate as employees change roles, take on new responsibilities, or leave the organization.
Effective HR data security therefore requires more than setting permissions once. Organizations need ongoing visibility into sensitive information and the access surrounding it.
How HR Data Access Problems Build Up
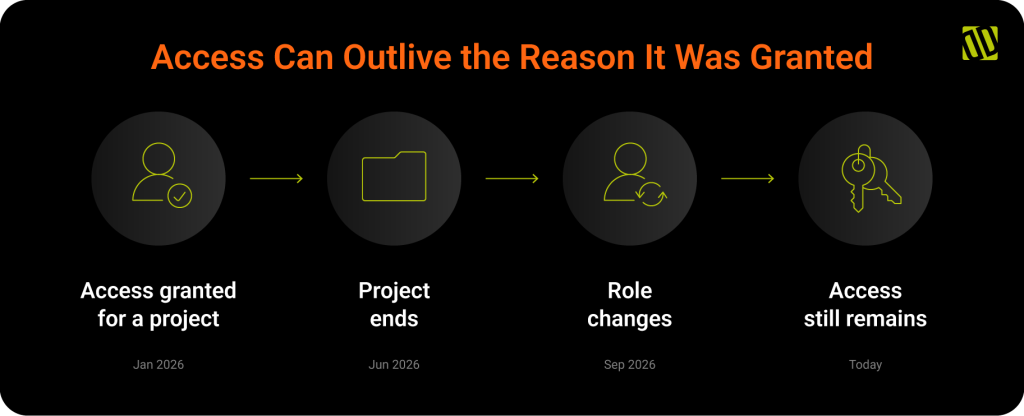
Consider a manager who receives access to employee records for a particular project or review. The access is appropriate at the time, but the project ends and the permission remains.
The same thing can happen when an employee changes roles but continues to have access to information required by their previous position. Over time, this kind of permission drift can leave organizations with access rights that no longer reflect current responsibilities.
The problem becomes more difficult as HR information grows and additional copies appear. A document may be downloaded, duplicated, moved to another folder, or stored on another system for a legitimate reason. Years later, it may be difficult to determine whether every copy is still necessary or appropriately protected.
In larger organizations, sensitive employee data can be spread across thousands or millions of files and multiple storage environments. The issue may not be that access controls are missing. Organizations may simply lack the visibility needed to confirm that those controls are still working as intended.
Why Employee Data Security Gets Harder at Scale
In a smaller organization, HR and IT teams may be able to identify the locations of sensitive information and periodically review access by hand.
That approach becomes far less practical across a large unstructured data estate. Traditional storage tools may provide information about capacity and location without answering the questions that matter most for employee data security:
- Where is sensitive employee information actually stored?
- Who owns a particular file?
- Who currently has access to it?
- Is that access still necessary?
- Are redundant or outdated copies creating unnecessary exposure?
Without those answers, teams are left relying on assumptions about where HR data should be stored and who should be able to reach it. Greater visibility allows HR, security, and IT teams to examine the information itself alongside relevant metadata. They can identify sensitive files across the wider environment, understand where those files reside, and determine who can access them.
Make Sensitive HR Data Visible
Once teams can see where sensitive HR data lives and how it is exposed, they have a stronger basis for deciding what should happen next.
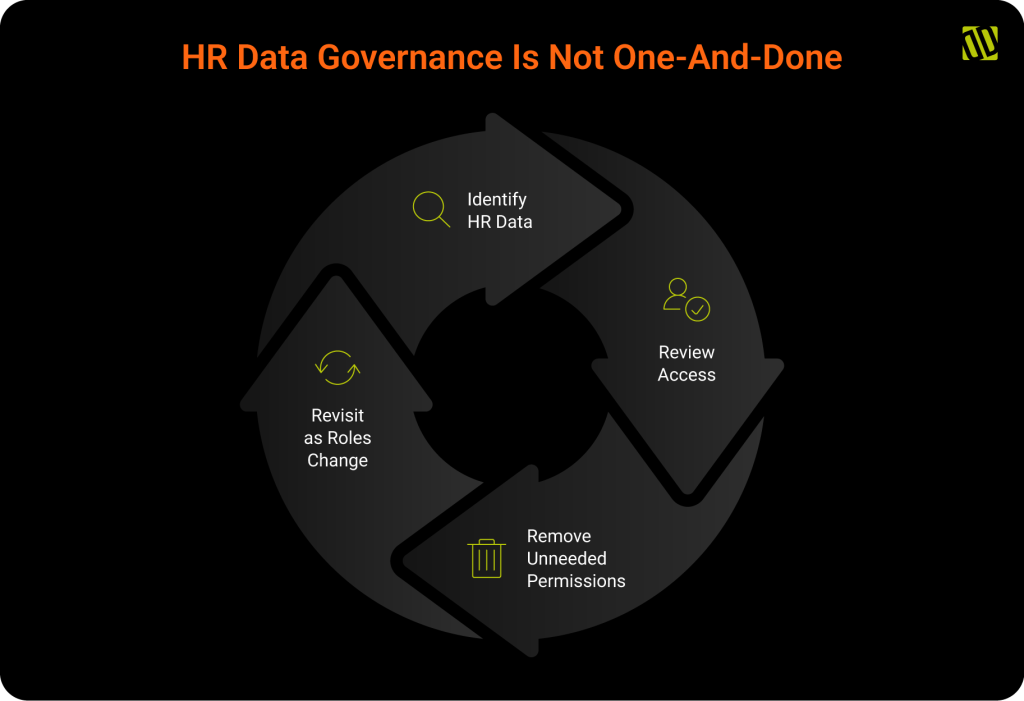
Permissions that are no longer necessary can be reviewed and removed. Redundant copies can be assessed. Files that should no longer be retained can be addressed according to the organization’s policies. Sensitive content stored in an inappropriate location can be identified for remediation. That visibility is particularly valuable because new confidential information is continually created and added to the data estate.
A point-in-time access review can only show conditions at that moment. Maintaining visibility over time gives teams a way to revisit access as circumstances change rather than discovering excessive access only after confidential information has already been exposed.
Reduce HR Data Exposure Before It Becomes a Problem
Sensitive HR files are one part of a much larger unstructured data estate. When organizations can identify sensitive, outdated, misplaced, or unnecessarily exposed data, they are better positioned to decide what should remain accessible and what should be secured, relocated, archived, or removed.
Download our brief, Manage the Blast Radius, to see how greater visibility into risky unstructured data can help organizations reduce unnecessary exposure and improve governance.
HR Data Security FAQs
HR data security is the protection of sensitive employee information from inappropriate access, exposure, loss, or misuse. Effective HR data security includes not only access controls but also ongoing visibility into where confidential information resides and whether current access remains appropriate.
Permission drift occurs when users retain access to information after the business need for that access has changed or ended. For example, an employee may keep access after completing a project or moving to a different role. Over time, these outdated permissions can increase unnecessary exposure.
Organizations can strengthen employee data security by identifying where sensitive HR information resides, understanding who owns and can access it, reviewing whether that access is still necessary, and addressing redundant, outdated, or improperly stored files. Because roles and data change continuously, access visibility should be maintained over time rather than treated as a one-time review.